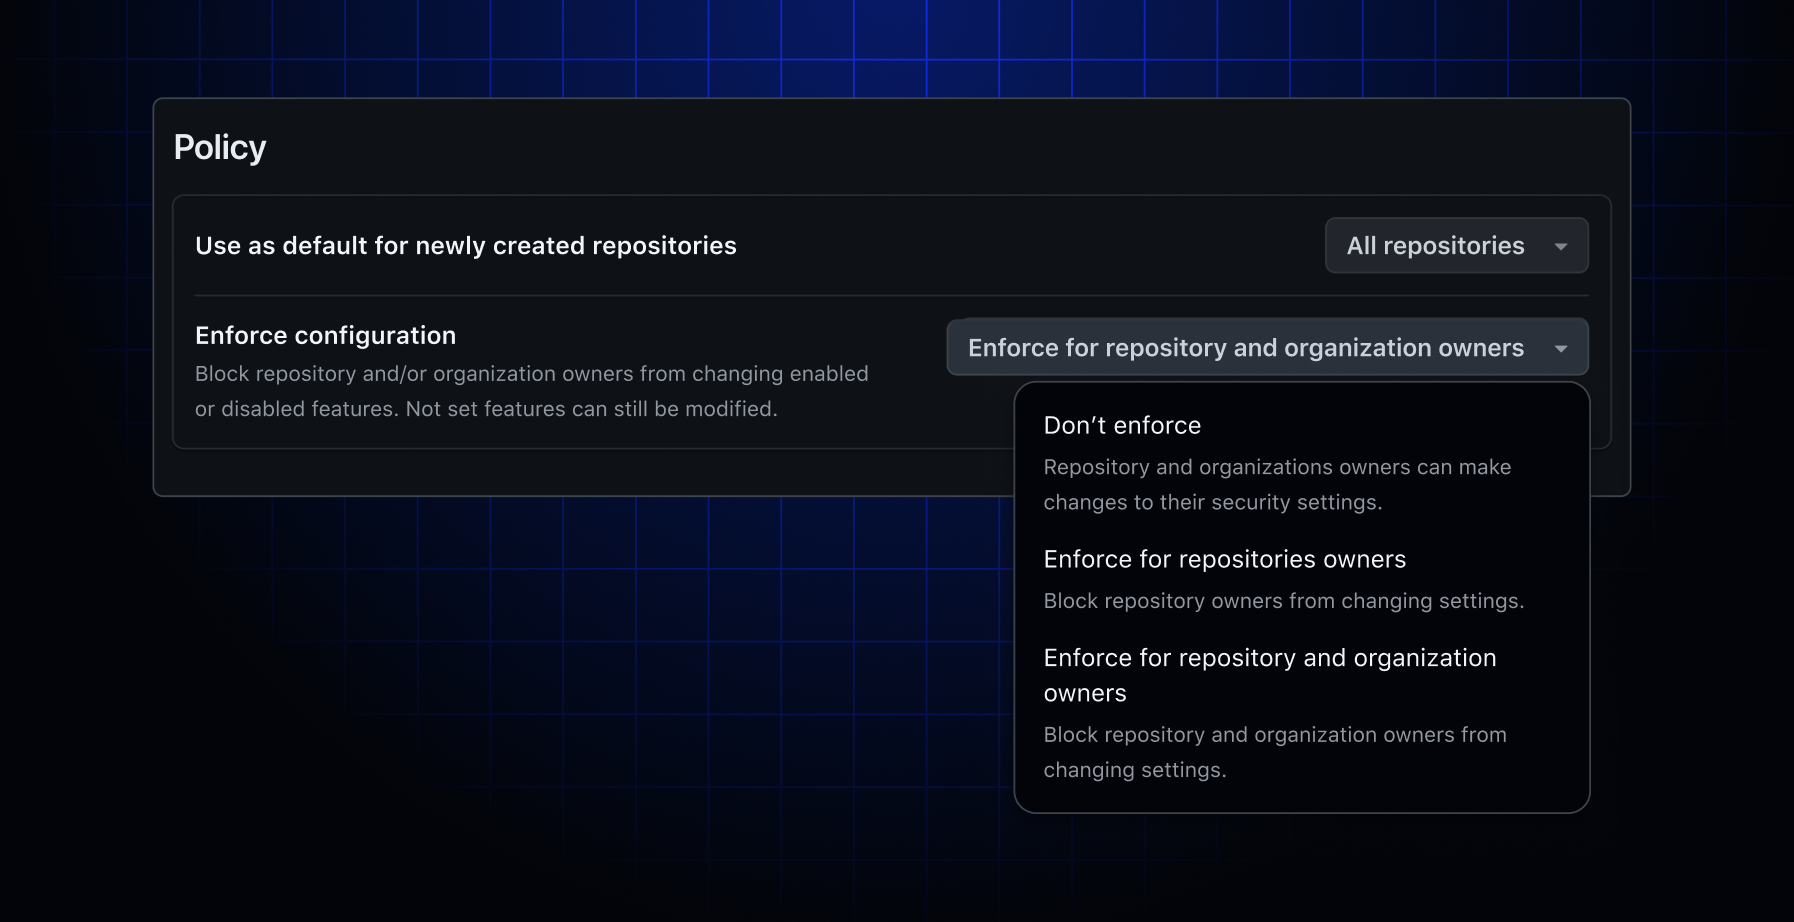
GitHub introduced a new enforcement option for GitHub Advanced Security configurations. Enterprise administrators can now apply security settings across their organizations and prevent lower-level administrators from overriding them.
The feature extends GitHub’s existing controls, which previously prevented repository owners from changing centrally defined settings. The new option can also block organization owners from modifying policies established at the enterprise level.
Administrators can choose among three enforcement modes: no enforcement, enforcement for repository owners, or enforcement for both repository and organization owners. The settings are configured within a security configuration.
The change is aimed at organizations that need consistent code-scanning and application-security policies across large repository fleets. Centralized enforcement can reduce configuration drift and help security teams demonstrate that required controls are applied uniformly, although teams will need governance processes for exceptions and policy changes.